
Another exchange hack has occurred—for the third time. This time, however, the amount involved was approximately USD 350 million, and the victim was Bitget.
In the early hours of September 25, 2026, Bitget experienced a sudden security incident. According to the security notice published by the platform, at 02:31:11 Beijing time, the system detected abnormal transfers from some hot and warm wallets, with a preliminary assessment indicating an amount of approximately USD 351.6 million involved; cold wallets were unaffected. Bitget stated that the relevant losses fall within the coverage of its user protection fund and temporarily suspended withdrawals, pending orderly resumption after security verification is completed.
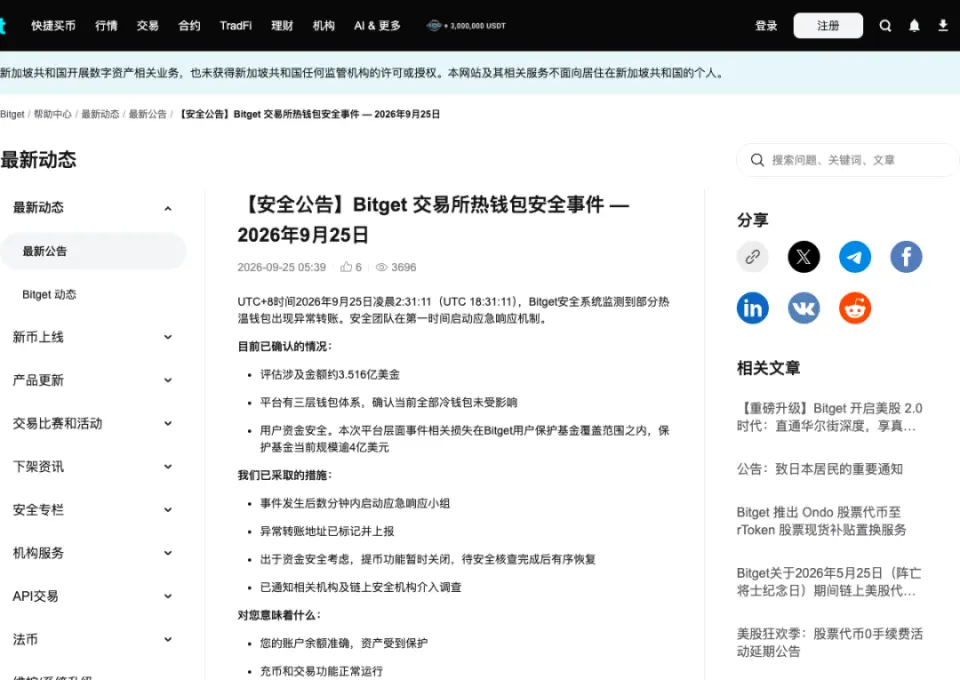
Security notice published by Bitget on September 25, 2026 (screenshot source: Bitget official website)
The more news of this kind I read, the harder it is for me to focus solely on "how much was lost again." The more practical questions are: through whose hands will the money pass next, and which participants still have time to do something? How the losses are compensated is first and foremost a test for Bitget; whether the funds can be intercepted also concerns the exchanges, exchange services, cross-chain protocols, aggregator applications along the way, and the people within them who actually hold operational authority.
After the incident, Bybit co-founder and CEO Ben Zhou expressed willingness to offer assistance to Bitget and said the team was updating the LazarusBounty platform to help trace the flow of the stolen funds. In a critical moment, a competitor was willing to extend a hand—such industry mutual assistance deserves recognition.
Similar mutual assistance has appeared in previous hacking incidents. After Bybit was hacked in 2025, Bitget CEO Gracy Chen publicly offered to assist with tracing and investigation. According to Bybit's official incident timeline, Bitget also transferred 40,000 ETH to Bybit at the time to provide liquidity support. Providing liquidity and recovering stolen assets are two different tasks, yet together they demonstrate one thing: after a major security incident, it is difficult for a single platform to complete all response measures on its own.
After the expressions of support, the truly difficult work begins. Stolen assets may be rapidly swapped into other tokens, split across multiple addresses, or bridged to another chain. Among the services the funds pass through along the way, some can control custodial accounts, some hold unsettled transactions, and some can only manage front-end access, routing, or part of the execution process. Investigators and the victim must identify as quickly as possible the entities that genuinely have the ability to take measures.
Collaboration on asset recovery truly tests three things:On-chain addressesWhether they can be matched to specific transactions, whether operational authority can be translated into disposal actions, and whether interim measures can be smoothly integrated into formal procedures.
These three matters also determine the order of discussion in this article. Public statements can convey goodwill; whether the funds can be intercepted requires answering, layer by layer, who controls this link, how far the transaction has progressed, what measures the available materials support, and how disclosure, preservation, and restitution will subsequently be completed.
Step one: first identify who actually holds disposal authority
To turn industry solidarity into action, the first step is to identify who holds actual authority over the relevant transactions. A service provider that receives assets, completes an exchange and then makes payment may control assets that have not yet been settled; a custodial exchange may hold authority over associated accounts and deposit and withdrawal permissions; and the operator of a cross-chain protocol or aggregator application may control only the front end, routing, transaction forwarding or part of the execution process.
In determining the counterparty for a mutual assistance request, the platform name and technical labels can only provide a starting point; what is truly useful is the business process and the control relationships.On this basis, the aggrieved party can identify entities capable of taking on the request; and an operator that receives a request can also confirm exactly what it is able to suspend, verify and preserve, and which matters fall outside its own authority.
Legal obligations must also be determined in light of the specific business and the applicable jurisdiction. Under the international standards of the Financial Action Task Force (FATF), virtual asset service providers should generally implement preventive measures such as customer due diligence, record keeping and suspicious transaction reporting, with the specific scope of application and manner of implementation given effect by the laws of each jurisdiction. Statutory verification, preservation or reporting obligations that have already been triggered should be performed in accordance with the applicable provisions; whether transactions may also be restricted or information provided to specific parties requires a separate determination.
This analysis applies equally to businesses that use decentralized technology. In its July 2026 thematic report on DeFi, the FATF focused on who has control over or sufficient influence over the relevant arrangements, and listed factors such as administrative authority, upgrade control, concentration of governance tokens and infrastructure influence. The report provides an analytical framework under international standards; specific obligations must still be referred back to local law. For cross-chain protocols and aggregator applications, what services the operator actually provides and which parts of the process it controls will usually be more informative than the label "decentralized."
Step Two: Map On-Chain Addresses to Specific Transactions
After identifying the entities that may take on the request, the next step is to map the on-chain fund path to the counterparty's accounts, orders and business records. Address labels can only indicate the direction of tracing; only when the matter is tied to specific transactions can the relevant operators more readily determine whether the funds remain within their control and what handling options exist at the current stage.
When an aggrieved platform or its authorized agent submits a mutual assistance request, it may, to the extent possible, explain the facts of the case, the blockchain involved, the transaction hash, the token, the amount, the time, the relevant addresses, and how these leads relate to the recipient's business. A service provider receiving the request may, in accordance with its own procedures, verify the identity of the requesting party, the source of the materials and the connection to its own transactions.The stage to which a transaction has been executed is an important lead for assessing the available handling options.
For services that receive funds first and then exchange and pay out, funds not yet exchanged, funds already exchanged but not yet paid out, and funds already paid out each correspond to a different control status. For cross-chain or aggregation services, the operator may, based on materials lawfully in its possession, check the source-chain transaction, the exchange request, the destination-chain address and the execution status. What specifically needs to be verified should be determined in light of the business architecture, the materials lawfully held and the applicable requirements.
Once external leads correspond to actual accounts, a custodial exchange may be able to take measures where it has the authority and a basis to do so. According to disclosures by Elliptic, in 2023 Binance and Huobi, based on intelligence provided by Elliptic, froze accounts containing approximately USD 1.4 million in crypto assets, with the relevant funds originating from the earlier Harmony Horizon cross-chain bridge attack. What made this case work was that the external tracing results corresponded to accounts controlled by the exchanges. Whether other platforms or protocols can take similar measures still depends on their respective authority, evidence and applicable procedures.
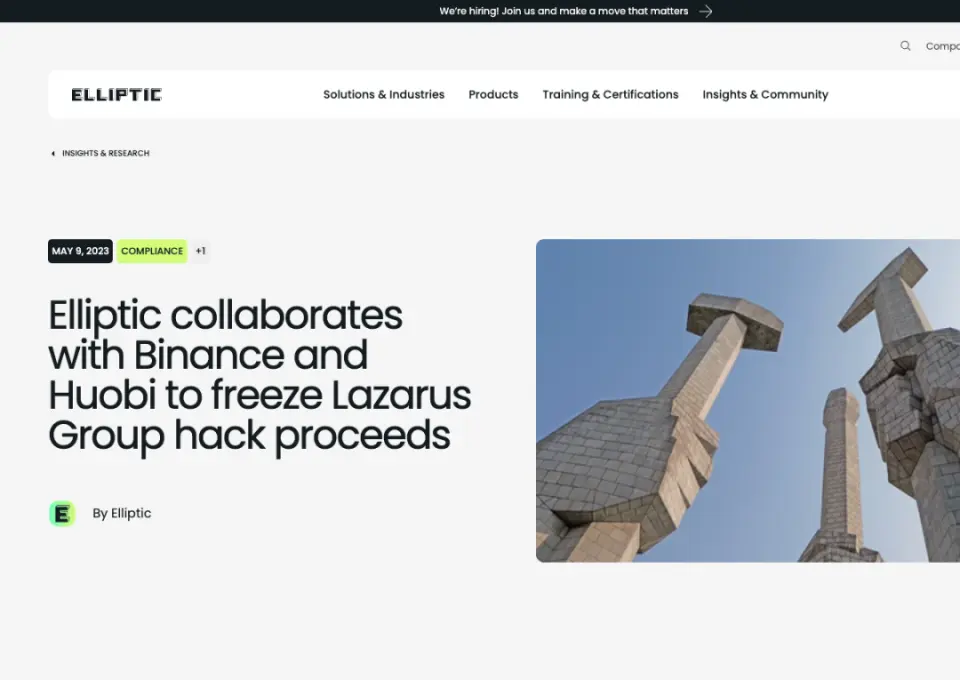
Elliptic disclosed that it collaborated with Binance and Huobi to freeze stolen funds associated with the Lazarus Group (screenshot source: Elliptic official website)
Step 3: Select appropriate measures according to the stage of the transaction
Once the leads are matched to specific transactions, the question shifts from "what has been found" to "what can still be done now." Restricting access points, suspending conversions, holding payments and restricting outbound transfers from escrow accounts differ in their objects of application, sources of authority and scope of impact. Operators need to make judgments among the urgency of continued fund flows, the credibility of the available materials and the rights and interests of ordinary transacting parties.
Where unsettled assets remain under the service provider's control, the service provider may, in light of applicable law, contractual arrangements, technical capabilities and the impact on the relevant users, assess the feasibility of suspending conversions or holding payments.The fact that a transaction has not yet been fully executed does not automatically give rise to an obligation to freeze or return assets, but it may leave time for temporary verification. Custodial exchanges, when faced with linked accounts, also need to examine the specific basis, scope and continuing conditions for restricting outbound transfers.
Operators of cross-chain protocols and aggregator applications should first map out which stages they control. Where they manage only the front-end interface, measures can usually affect only that access point; where they also hold transaction forwarding or execution authority, other room for intervention may exist. Where contract suspension or upgrades are involved, multisignature arrangements, governance procedures and the impact on other users will also affect whether a measure is feasible.
Access-point restrictions can reduce the risk that a particular service will continue to be exploited, and their practical effect depends on the service architecture and other access paths.If users can still access the service through other entry points or by calling the contract directly, the effect of restricting a single front end will be relatively limited.
OKX's announcement dated 17 March 2025 provides a real-world example. OKX stated that, after discovering that Lazarus was attempting to abuse its DeFi services, it proactively suspended its DEX aggregation service and upgraded its preventive measures following communication with regulators; the announcement also stated that the aggregator connects liquidity across multiple protocols and does not itself custody client assets. This case shows that non-custodial services can also adjust the products and entry points they control. Whether funds in the underlying protocols can be frozen still depends on the actual architecture and control authority.
When relevant operators adopt temporary measures, they may also consider in parallel the scope of application, review milestones, conditions for lifting the measures and record retention. Law enforcement or judicial orders that are legally binding and applicable to the operator should be handled in accordance with their effect and scope; where there are doubts about the scope of execution or technical feasibility, the operator may explain the matter and seek clarification through the appropriate procedures. Even if the funds have already been transferred out, lawfully retained account, order, login and communication records may continue to assist subsequent recovery efforts.
Step 4: Connect temporary restrictions to formal return procedures
Stopping the funds temporarily only buys a window for handling the matter. Whether they can ultimately be returned still requires answering who owns the assets, what can be delivered, to whom delivery should be made and under what procedures delivery should occur. After conversions and multiple transfers, the counterparty to a transaction may assert its own basis for lawful trading and acquisition of the assets; once the funds enter an exchange's pooled funds, the party seeking recovery may also need to further prove the connection between the controlled assets and the originally stolen funds.
Temporarily restricting transfers and final return often correspond to different conditions and evidentiary requirements.An entity that only manages the front end and does not control the relevant assets may be able to assist mainly by providing records it lawfully holds; an entity that holds customer information or order information must also consider, when disclosing externally, the recipients, the scope of disclosure, confidentiality obligations and personal information protection requirements.
Judicial measures also require the party pursuing recovery to have its evidence and procedures in order. In the 2023 judgment in the UK Piroozzadeh case, the victim obtained an interim property injunction without notifying Binance, and the court later set aside the injunction because the applicant had not presented the case fully and fairly. The judgment discussed the defence of bona fide purchase for value that an exchange might raise, and how to identify and enforce preservation measures after funds are commingled in a pool. The case concerned an application for an interim injunction and did not make a final determination on the ownership of the assets, but it reminds parties pursuing recovery that, for on-chain tracing results to be converted into judicial measures, the corresponding evidentiary and procedural requirements must still be met.
The public rules of exchange services can also reflect this distinction. ChangeNOW's public guidance on cooperation requests requires the requesting party to provide information on the facts of the case, the transactions, the list of addresses and the law enforcement procedure; Article 6.11 of its terms of service further states that, depending on when the report is received, the platform may intercept a transaction only after the exchange has been completed, in which case the assets that can be returned may be in the post-exchange currency. Under that provision, return also requires an explicit request from law enforcement authorities. This is the handling mechanism publicly disclosed by ChangeNOW; how other service providers handle such matters still depends on the applicable law, contractual arrangements, the status of the assets and the specific procedures.
What different participants should do first, respectively
When the foregoing analysis is put into practice, the greatest concern is that "everyone is willing to help, but no one knows who should send the next email, what should be attached, or to whom the matter should be referred for assessment once received." The flow of funds will not wait for the parties to become familiar with the process. In light of the authority of different roles, the following matters may serve as a reference when initiating handling.
For the victim platform or project party:Priority may be given to fixing the timeline of the incident, compiling the transaction hashes, the addresses involved, the currencies, the amounts and the on-chain paths, and preparing ownership, reporting and authorization materials. Requests for external cooperation should preferably be sent through a single window, clearly stating what the other party is asked to verify, the extent to which the existing leads support the matter, and how the subsequent formal procedures are being advanced.
For operators such as exchanges and exchange services:After receiving leads, the related accounts, orders and transaction stages may first be checked, and KYC, login, device, communications and operation records preserved; business, technical, compliance and legal personnel may then assess the measures that can be taken in light of their own authority. Matters not yet confirmed may be described as still under review; measures already taken and their limitations may also be fed back to the requesting party to the extent that communication is permitted by law.
For cross-chain protocols, aggregators and related operators:The smart contracts, front end, routing, API, upgrade permissions and governance mechanisms may be distinguished as soon as possible to confirm which parts are actually under the entity's control. Before adjusting entry points, suspending services or initiating multisignature or governance procedures, the entity should also assess other access paths, the impact on ordinary users and the conditions for restoration, and retain the facts and authority explanations on which the decision was based.
For lawyers and on-chain investigation teams:The focus of the work is to organize the on-chain trail into a factual record that platforms, law enforcement agencies and courts can all understand, and to map each request to a specific entity, authority and procedure. Where multiple jurisdictions or multiple service providers are involved, the transmission of materials and the sequence of actions must also be designed, so that leads do not remain confined to a list of addresses, and so that interim restrictions do not become disconnected from subsequent preservation, disclosure and restitution.
The earlier all parties collaborate on the same factual record, the easier it is to connect verification, restriction, disclosure and restitution.Relevant operators may also, in ordinary course, establish a channel for risk leads and internal decision-making procedures, clarifying who receives requests, who determines whether a transaction is connected, who assesses the legal basis, and in what circumstances escalation to management or an external professional team is required.
Whether liability is borne ultimately still depends on the specific evidence
Only after collaboration moves forward can questions of liability be discussed more accurately. A delayed response, an error in risk assessment, a continuing violation of statutory anti-money laundering requirements, and knowingly assisting the transfer of criminal proceeds each correspond to different facts and legal assessments. For protocols or applications, liability must also be attributed to a specific operator or controller; status as a developer, governance participant or the like is not in itself sufficient to establish liability directly.
At the regulatory level, it must first be confirmed whether the relevant entity is an obligated entity under the applicable law, and only then can the specific customer due diligence, record-keeping and reporting requirements be determined. The FATF standard on suspicious transaction reporting requires states to provide by law that financial institutions report promptly to the financial intelligence unit where they suspect or have reasonable grounds to suspect that funds are the proceeds of crime. For virtual asset service providers subject to local law, the reporting entity, triggering conditions and manner of performance remain governed by local rules.
Submitting a suspicious transaction report to a statutory authority and disclosing customer information to an injured party are two different types of conduct, with different bases and boundaries. Reported information may also be subject to confidentiality restrictions. Whether the relevant operator may state externally that a report has been made or that an investigation is underway must be determined in light of the applicable rules; more serious allegations, such as assisting money laundering, must be proven by evidence as to the specific conduct, subjective knowledge and other elements required by local law.
In the 2025 investigation by German law enforcement authorities into the crypto asset exchange service eXch, attention was directed both to the flow of funds and to the platform's mode of operation. Elliptic had traced and found that some of the ETH stolen from Bybit was exchanged into BTC through services including eXch. Subsequently, the German Federal Criminal Police Office announced that on April 30, 2025, law enforcement authorities seized eXch's servers in Germany and crypto assets then worth approximately EUR 34 million, and that the operators were suspected of commercial money laundering and of operating an internet platform for criminal transactions. The announcement also stated that the service had advertised on the dark web that it did not apply anti-money laundering measures and did not require users to verify their identity. The criminal allegations concerned must still be proven in accordance with the legal elements and evidence.
The lesson from this case is direct: investigating authorities look not only at where funds passed through, but also at how a service solicited business, how it organized exchanges, and what action it took when faced with risk leads.Operators retaining necessary verification and decision-making records helps to explain when risks were identified, what authority they held at the time, and why a particular measure was or was not taken.The scope of records and retention periods must still comply with applicable rules, and their probative value must also be assessed together with other evidence.
Mankun Lawyers' Summary
Having seen many similar incidents, I increasingly believe that the outcome of asset recovery often depends on a very simple matter: whether the parties can, in the shortest possible time, connect authority, evidence and procedure together. Public expressions of support can show the industry's warmth; but actually stopping assets, getting materials into an investigation, and giving restitution a basis still require concrete work item by item.
The hardest part of matters of this kind is usually piecing together on-chain paths, account and order information, business control authority, legal basis and cross-border procedures into an enforceable recovery chain. The earlier on-chain investigators, platform compliance teams, technical personnel and lawyers collaborate around the same factual record, the easier it is for subsequent verification, restriction, disclosure, preservation and restitution to connect. For institutions where abnormal asset transfers have already occurred, or which may receive assistance-investigation requests, completing an authority review, evidence preservation and response-path design at an early stage can also reduce the risk of missing the window for handling.
What users entrust to a platform is assets, and also trust. The true sign of industry maturity is that, after every incident, publicly expressed goodwill can be translated into action that has a basis, is enforceable and leaves a traceable record.
I hope that in the future we see less of another "again" and more of an evidence-supported "it has been recovered."

